DPDPEnforced May 13, 2027Start free →
SOVEREIGN CONSENT ARCHITECTURE |DPDP ACT 2023 · GDPR · CCPA/CPRA
++++
STATUTORY CONSENT MANAGEMENT ENGINE

Automated consent management engineered for India’s DPDP Act.

Deliver unbundled itemised notices in 22 Eighth Schedule Indian languages, block ad pixels before affirmative consent, and anchor tamper-evident audit receipts into sovereign Merkle trees.

22Indian Languages
< 12 KBZero-Dependency SDK
100%Pre-Consent Blocking
AWS Mumbaiap-south-1 Residency
SYSTEM SPECIFICATION

Architectural overview of the sovereign consent engine

Engineered as a high-performance infrastructure layer designed specifically for modern engineering teams and compliance officers:

Sub-12KB Zero-Dependency Autonomous SDK

Loads asynchronously in less than 35 milliseconds. Does not block DOM rendering or trigger layout shifts, protecting your Google Core Web Vitals and LCP scores.

22 Eighth Schedule Multilingual Notice Engine

Instantly render statutory notices in Hindi, Bengali, Tamil, Telugu, Marathi, Gujarati, Kannada, and 15 additional constitutional languages under Section 5(3).

HMAC-SHA256 Cryptographic Audit Ledger in AWS Mumbai

Guarantees 100% Indian data localization in AWS Mumbai (ap-south-1). Produces tamper-evident Merkle tree inclusion proofs to satisfy Section 6(10) audit inquiries.

DEFINITIVE ARCHITECTURE

What is modern consent management under the DPDP Act 2023?

Consent management is the governance framework that allows organizations to collect, record, honor, and prove an individual’s privacy choices.

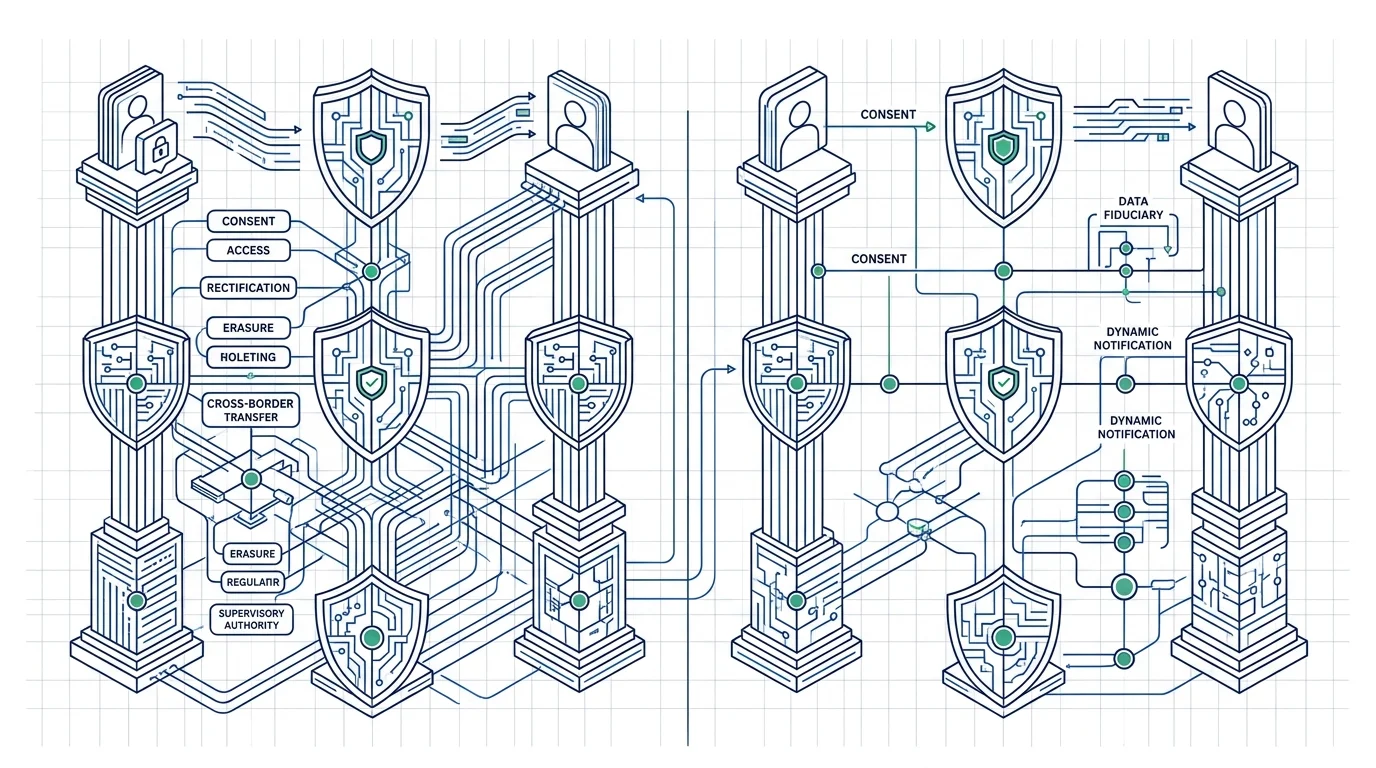
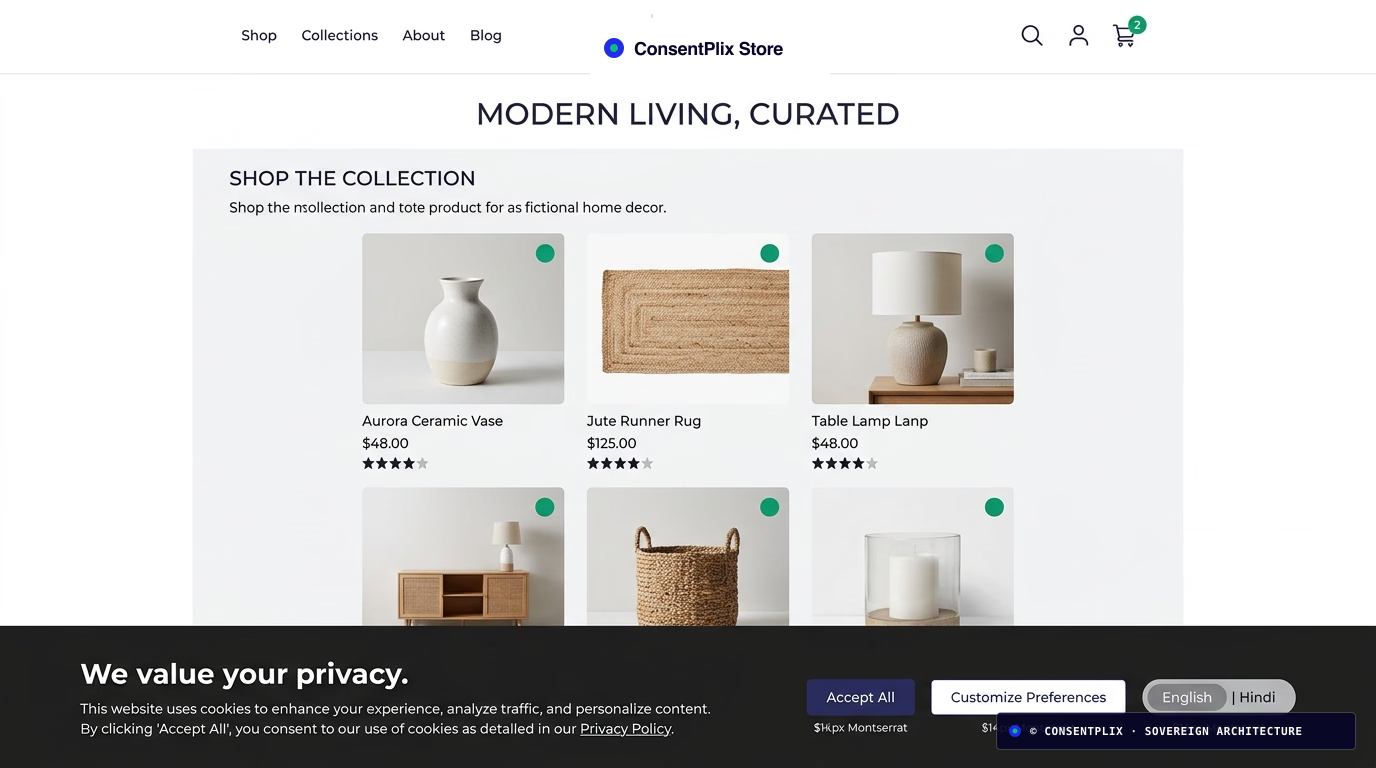
Under India’s DPDP Act 2023, simple "Accept Cookies" banners are legally invalid. The law mandates that consent must be free, specific, informed, unconditional, and unambiguous with a clear affirmative action under Section 6(1).

Statutory Definitions & Fiduciary Obligations

Section 6(1): Free, Specific, Informed, Unconditional & Affirmative Consent

Consent cannot be bundled into Terms of Service or assumed via page scrolling. Pre-ticked checkboxes and silent cookie drops are prohibited.

Section 6(10): Reverse Burden of Proof on Data Fiduciaries

If a user disputes consent before the Data Protection Board of India, the business must produce mathematically tamper-evident proof of valid consent.

Section 5(3) & 6(3): Multilingual Language Mandate

Data Principals must be given the option to access the notice and consent agreement in English or any of the 22 languages specified in the Eighth Schedule.

Core Pillars of the Sovereign Consent Architecture

Each pillar solves a statutory compliance duty while preventing revenue disruption to analytics and paid ad campaigns.

+

22 Scheduled Languages

Give users the option to review notices in English or any Eighth Schedule Indian regional language under Section 5(3) & 6(3).

+

Pre-Consent Ad Blocking

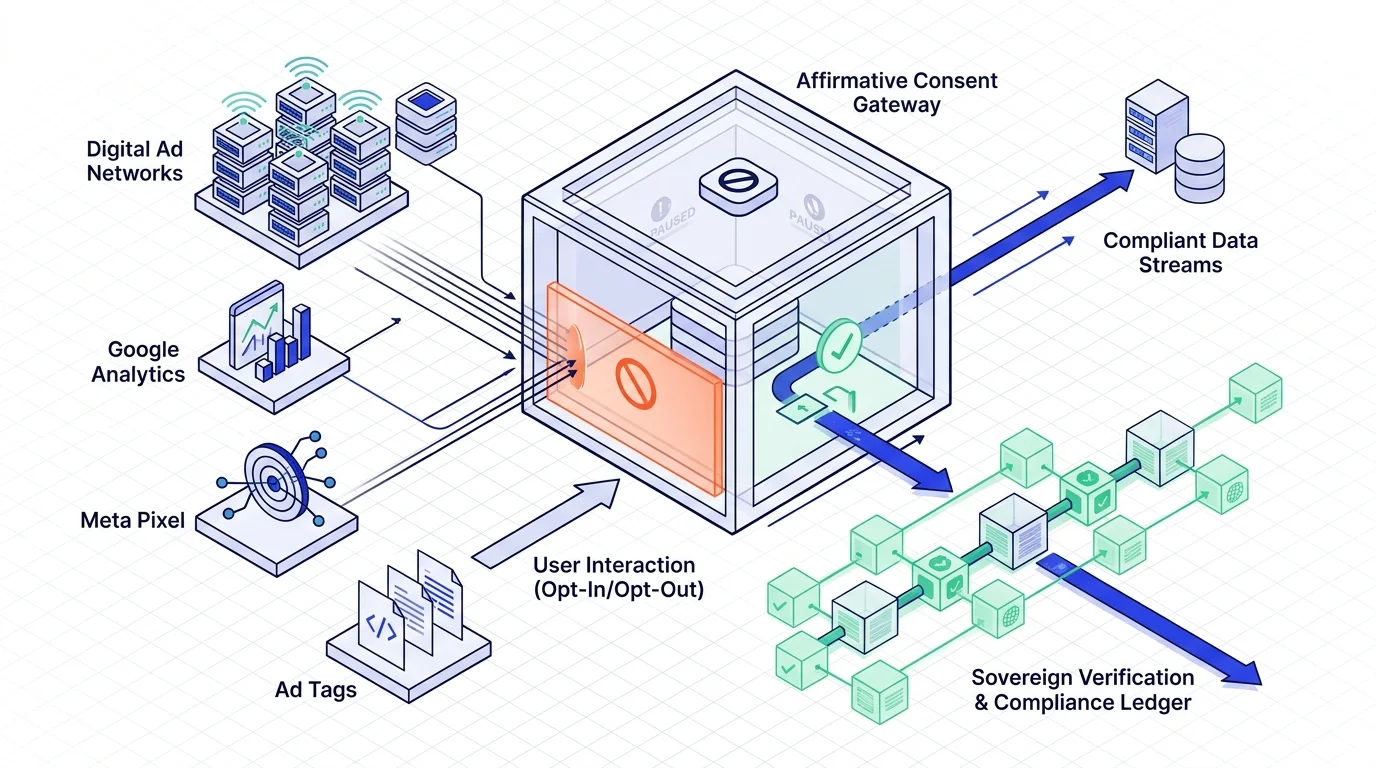
Pause Google Ads, Meta Pixel, and analytics tags asynchronously until the user chooses. See consent before ads guide.

+

Merkle Audit Ledger

Every event is signed via HMAC-SHA256 and batched into append-only Merkle trees in AWS Mumbai. Read our cryptographic ledger brief.

+

Symmetrical Withdrawal

Under Section 6(4), revoking consent must be as effortless as granting it via a single-click persistent footer preference drawer.

END-TO-END WORKFLOWTHE 5 STAGES OF STATUTORY CONSENT MANAGEMENT
LIFECYCLE BLUEPRINT

The 5 stages of the statutory consent management lifecycle

A compliant consent management system oversees every interaction between the user, their browser, third-party marketing tags, and your backend records:

01

Notice Presentation & Purpose Itemisation

Section 5 & 6(1)

Deliver a standalone notice detailing itemised processing purposes in English and regional Indian languages under Section 5.

Unbundled Toggles
02

Pre-Consent Script Interception & Ad Gating

Google Consent Mode v2

Marketing pixels and cookies remain strictly locked until the user performs a deliberate affirmative action.

Zero Pre-Consent Drops
03

Cryptographic Sealing & Merkle Ledger Ingestion

Section 6(10) Proof

Every granted or denied toggle produces a signed canonical receipt anchored into a sovereign Merkle tree.

HMAC-SHA256 Hash
04

Symmetrical Withdrawal & Preference Updates

Section 6(4) Duty

Users adjust preferences or withdraw consent with a single click from your footer, instantaneously updating tag firing.

1-Click Persistent Drawer
05

Rights & Grievance Redressal Automation

Sections 11–14

Automate Data Principal requests for access, correction, erasure, and grievances under statutory resolution windows.

Self-Serve Rights Portal
TECHNICAL COMPARISON

Comparative architecture: ConsentPlix vs legacy European CMPs

Most consent software was engineered for Europe’s ePrivacy directive. See why Indian businesses need an architecture designed DPDP-first. Read our detailed guides on DPDP vs GDPR and the best DPDP CMP tools.

Regulatory Alignment & Grounds

DPDP Act 2023 vs EU GDPR

European CMPs rely heavily on "legitimate interest" exceptions for ad tracking. DPDP provides zero legitimate interest defenses for marketing cookies, requiring strict affirmative consent under Section 6(1).

Security & Evidentiary Proof Standards

Cryptographic Receipts vs SQL Logs

Legacy CMPs store consent choices in mutable MySQL tables that fail forensic scrutiny. ConsentPlix anchors HMAC-SHA256 receipts into immutable binary Merkle trees in AWS Mumbai.

Web Performance & Core Web Vitals

Sub-12KB Single File vs 100KB+ Bloat

Traditional enterprise CMPs load 60KB to 150KB of blocking JavaScript that delays Largest Contentful Paint (LCP) by up to 1.8 seconds. ConsentPlix executes autonomously in sub-12KB.

Statutory RequirementConsentPlix Sovereign CMPLegacy Cookie Banners (OneTrust, CookieYes)
22 Eighth Schedule Indian LanguagesBuilt-in Native Language SwitcherEnglish & European languages only
Section 6(10) Burden of ProofHMAC-SHA256 Cryptographic Merkle ReceiptsMutable browser cookies / MySQL logs
Pre-Consent Script InterceptionAutomated Asynchronous BlockingManual developer tagging required
Script Weight & Core Web Vitals< 12 KB (Zero External Dependencies)60 KB – 150 KB (Delays LCP by up to 1.8s)
Google Consent Mode v2Native Turnkey Signal IntegrationComplex custom GTM setups
Data Residency & Sovereign CloudStrict AWS Mumbai (ap-south-1)Mixed US / EU cloud zones
Self-Serve Starting PriceFree Forever / ₹399 per monthHigh enterprise quotes (₹5L+ per year)
TECHNICAL IMPLEMENTATION

How to implement consent management on your website

A four-step deployment blueprint for software engineers and website administrators:

STEP 01

Audit Trackers & Third-Party Ad Pixels

Tracker Inventory & Cookie Classification

Identify all third-party analytics, retargeting tags, customer support chat widgets, and social pixels loading on your website. Classify them into strictly necessary, analytical, and marketing purposes.

Pro tip: Run our free DPDP Website Scanner to discover hidden tracking cookies.
STEP 02

Generate Purpose-Specific Statutory Notices

DPDP Section 5 Multilingual Drafting

Draft an itemised notice detailing the specific personal data collected, specific processing purposes, Data Protection Officer (DPO) contact details, and the right to withdraw under Section 6(4).

Use our DPDP Privacy Notice Generator for compliant statutory copy.
STEP 03

Deploy the ConsentPlix SDK Script Tag

Single-Line Asynchronous Head Embed

Paste the sub-12KB autonomous embed before any advertising scripts in your HTML <head>. The SDK automatically sets default denied signals in Google Consent Mode v2.

<script src="https://cdn.consentplix.com/sdk.js" data-site="YOUR_ID" async></script>
STEP 04

Configure Webhooks & Rights Portal

Automating Withdrawal & Erasure (§11–§14)

Connect ConsentPlix webhooks to your CRM or marketing databases to ensure that when a customer revokes consent or requests erasure, their records are scrubbed across your systems.

Explore the Rights Portal Overview and API documentation.
STATUTORY RISK MANAGEMENT

DPDP Act penalty structure under The Schedule

Financial penalties under the DPDP Act 2023 are non-negotiable statutory caps administered by the Data Protection Board of India. Review our analysis of The Schedule penalties:

THE SCHEDULE · ITEM 4

General Consent & Notice Breach

Up to ₹50 Crore

Residual statutory penalty cap under the Schedule for failing to give valid notice, bundling consent, or obstructing withdrawal under Section 6.

THE SCHEDULE · ITEMS 2 & 3

Children’s Data & Breach Notice

Up to ₹200 Crore

Penalties for behavioral tracking or targeted ads directed at minors under 18 (Section 9(3)), or failing to notify a personal data breach (Section 8(6)).

THE SCHEDULE · ITEM 1

Security Safeguard Failure

Up to ₹250 Crore

Strictly reserved for failing to implement reasonable security safeguards to prevent a personal data breach under Section 8(5).

CMS & FRAMEWORK SUPPORT

Consent management integrations across popular CMS platforms

One script tag integrates full DPDP, GDPR, and CCPA consent gating across your existing tech stack:

E-COMMERCE & D2C

Shopify DPDP Banner

Theme.liquid Gating

Block Google Ads and Meta Pixel before consent in theme.liquid without hurting conversions or store speed.

Read Shopify Tutorial
CONTENT & WOOCOMMERCE

WordPress DPDP Plugin

22 Indian Languages

Replace outdated GDPR plugins with full 22 Indian regional languages and hosted Rights Portal for WordPress.

Read WordPress Tutorial
NO-CODE DESIGN

Webflow DPDP Integration

Custom Code Embed

Paste the sub-12KB embed directly into Webflow Project Settings with native styling and preference drawers.

View Webflow Solution
MODERN STACK

React & Next.js

SSR & Edge Middleware

Integrate via NPM package with zero hydration mismatch and edge geolocation middleware support.

Read Quickstart Guide
CONSENT LIFECYCLE & CHAIN OF CUSTODY

From banner click to audit-ready, tamper-evident proof

ConsentPlix intercepts tracking scripts before execution, captures unambiguous visitor decisions through itemized statutory notices, computes an HMAC-SHA256 signature across 11 canonical fields, and anchors the record into daily Merkle checkpoint roots. Every event yields a tamper-evident, independently verifiable audit receipt.

Script InterceptionPRE-TAG INGRESS

Zero-Delay Script Interception

0ms Main Thread Delay · Pre-GTM Execution

Sub-12KB autonomous SDK loads deterministically before Google Tag Manager and third-party ad pixels fire. Holds non-essential trackers in queue until affirmative consent is given.

GTM SCRIPTHELDAUTHORIZED
<script src="cp.min.js" data-site-token="..."></script>< 12 KB IIFE
Statutory Notice22 CONSTITUTIONAL LANGUAGES

Verifiable Statutory Notice

Zero Pre-Ticked Toggles · One-Click Revoke

Renders clear, itemized notice in English and all 22 Eighth Schedule Indian languages. Discloses the Grievance Redressal Officer with instant Section 6(4) withdrawal.

22 LANG
NO DARK PATTERNSCOMPLIANT
Cryptographic SignatureRFC 2104 · SHA-256

HMAC-SHA256 Signed Artifact

11 Canonical Fields · KMS Key Custody

Every consent grant, refusal, or revocation is canonicalized across 11 fields and signed in hardware HSMs. Produces an unforgeable receipt code for legal audit.

HASH9f83…d71b
BURDEN OF PROOF COMPLIANTHMAC VERIFIED
Merkle Root SealRFC 6962 · DAILY ANCHORING

Merkle Checkpoint Proof Vault

Immutable Append-Only · Zero Retroactive Rewrite

Daily cryptographic Merkle tree roots seal the consent vault. Any auditor or judge can mathematically verify that a specific receipt existed on a given date without leaking customer identity.

MERKLE ROOTBRANCHBRANCH
LATEST ROOT: 9a410c2d...8b31 · AWS AP-SOUTH-1SEALED
DPDP CONSENT CLOUD · PREDICTABLE PRICING

Predictable pricing for audit-ready consent proof.

Every plan includes the sub-12KB autonomous SDK, cryptographically signed consent receipts, immutable audit trails, and sovereign hosting in AWS Mumbai (ap-south-1).

Non-Disruption Guarantee (DPDP Act §6 & §8(6)): Consent banner presentation and HMAC cryptographic verification never stop, even if quotas are exceeded.
FREE FOREVER · ZERO COST

Free Forever

Evaluation & Hobby

Evaluate DPDP compliance with zero commitment on single websites and personal apps.

₹0
Free forever · No credit card required
1,000 Consents · 1 Domain

Included Capabilities

  • 1 production domain
  • 1,000 consent events per month
  • Standard DPDP compliant notice banner
  • English & Hindi notice translations
  • HMAC-SHA256 signed audit trail
  • 30-day immutable consent ledger
  • Public receipt verification (/receipt)
  • Hosted sovereign in AWS Mumbai
POPULAR · D2C

Starter

D2C & Single Brand

For D2C brands, developers, and single-store sites building custom consent user interfaces.

₹399/ month + GST
25% discount available on annual billing
10,000 Consents · 1 Domain

Included Capabilities

  • 1 production domain
  • 10,000 consent events per month
  • Headless Pro Consent Studio (Custom UI & REST API)
  • All 22 scheduled Indian languages
  • 180-day cryptographic audit ledger
  • Advanced banner theme customizer
  • Data Principal rights portal (/rights)
  • Offline intake & QR code generator

Growth

Multi-Brand & Scale

For scaling platforms, multi-brand e-commerce and companies requiring automated audit defense.

₹999/ month + GST
25% discount available on annual billing
50,000 Consents · 5 Domains

Included Capabilities

  • Up to 5 production domains
  • 50,000 consent events per month
  • Full Headless Pro Consent Studio
  • Scheduled automated cookie & script scanner
  • GTM Container JSON one-click export
  • Signed DPBI legal audit dossier export (ZIP)
  • Incident & breach notification ledger
  • 365-day cryptographic retention
SDF COMPLIANCE READY

Enterprise

Significant Data Fiduciaries

For high-volume brands, BFSI, and Significant Data Fiduciaries requiring dedicated VPC custody and SLA.

Custom
Tailored volume pricing · Dedicated tenancy
1,000,000+ Consents · Unlimited

Included Capabilities

  • Unlimited domains & subdomains
  • 1,000,000+ monthly consent events
  • Statutory GRO portal (DPDP §8(6))
  • Native real-time webhooks & lake streaming
  • Cross-domain consent synchronization
  • 3-Year statutory retention ledger
  • Guaranteed Mumbai residency (Dedicated VPC)
  • Dedicated compliance manager & 99.99% SLA
GST @ 18% with full B2B Input Tax Credit invoices under SAC 998313 (India).Compare full feature matrix & surge packs
FREQUENTLY ASKED QUESTIONS

Frequently asked questions about consent management

What is consent management?

Consent management is the systematic process by which businesses present transparent privacy notices, obtain legally valid affirmative opt-in consent from individuals before collecting their personal data, record auditable consent choices, and allow users to easily manage or withdraw their consent at any time. Under modern data privacy laws like India’s DPDP Act 2023 and the EU GDPR, consent management is a mandatory statutory obligation, not an optional feature.

What is a Consent Management Platform (CMP)?

A Consent Management Platform (CMP) is a software solution that automates the consent lifecycle on websites and mobile apps. It delivers customizable consent banners, blocks third-party advertising scripts and cookies prior to consent, synchronizes consent signals with platforms like Google Consent Mode v2, and maintains tamper-evident audit records to satisfy regulatory burden of proof requirements.

How does consent management under the DPDP Act differ from European GDPR?

While GDPR permits businesses to process tracking cookies under commercial "legitimate interests", India’s DPDP Act 2023 requires explicit, affirmative opt-in consent under Section 6(1) with no legitimate interest defense for ad tracking. Furthermore, DPDP mandates standalone notices with the option of 22 Eighth Schedule Indian languages (§5(3)), places the reverse burden of proof on the fiduciary (§6(10)), and establishes a statutory Consent Manager intermediary framework (§2(g)).

Why is pre-consent script blocking mandatory in consent management?

Under Section 6(1) of the DPDP Act 2023, data processing before affirmative consent is granted is unlawful. A consent banner that permits Google Analytics, Meta Pixel, or ad tags to execute on page load before the user clicks "Accept" violates statutory requirements, exposing the fiduciary to penalties of up to ₹50 crore under the Schedule.

How does ConsentPlix prove consent during a regulatory audit?

ConsentPlix uses an append-only cryptographic ledger. Each consent interaction generates an HMAC-SHA256 signed event anchored into a binary Merkle tree hosted in AWS Mumbai (ap-south-1). During an inquiry by the Data Protection Board of India, legal counsel can export verifiable inclusion proofs that mathematically demonstrate the exact notice version, timestamp, language, and choices made by the user.

Can ConsentPlix manage consent across multiple jurisdictions (DPDP, GDPR, CCPA)?

Yes. ConsentPlix uses zero-latency edge CDN geolocation to detect visitor origin. Indian visitors receive DPDP Act Section 5 notices with 22 regional language options; European visitors see granular GDPR opt-in modals; and California visitors receive CCPA/CPRA Do Not Sell opt-out notices and Global Privacy Control (GPC) auto-detection.

EDITORIAL & PRIVACY ENGINEERING

Latest Insights & Technical Architecture

Authoritative briefings on DPDP Act enforcement, cryptographic ledger design, and autonomous SDK performance from our engineering team.

ENTERPRISE READINESS

Ready to deploy provable consent infrastructure?

Deploy in minutes with our sub-12KB SDK or schedule a customized technical consultation with our privacy engineering team.